CloudConnexa + Intune: Zero-Trust Remote Access
Build zero-trust remote access with CloudConnexa, free. Then wire SAML to Entra ID and push OpenVPN Connect through Intune with the Cloud ID pre-filled.
Build zero-trust remote access with CloudConnexa, free. Then wire SAML to Entra ID and push OpenVPN Connect through Intune with the Cloud ID pre-filled.
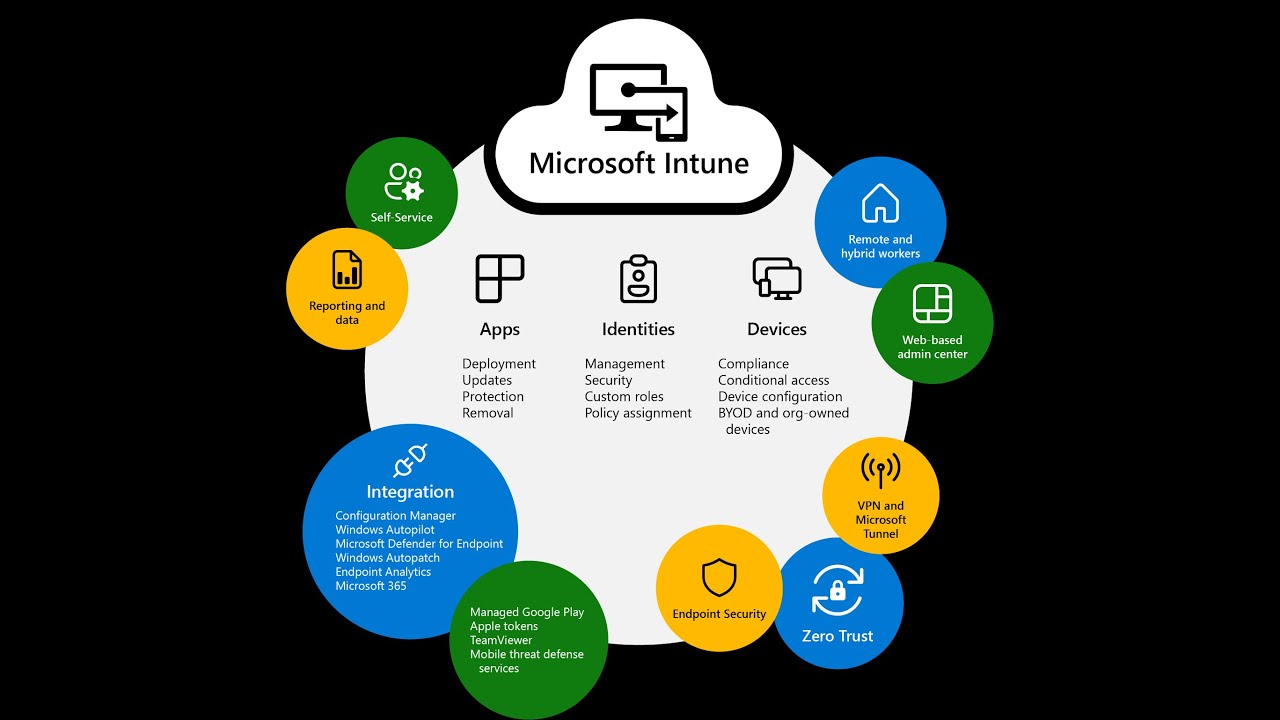
Move from on-premises AD to Entra ID with Intune: an Autopilot profile and dynamic device group, GPO import via Group Policy analytics, apps and hashes.
Connect on-premises AD to Microsoft Entra ID with Cloud Sync: custom domain, provisioning agent, scoping filters, group licensing, SSPR and Seamless SSO.
Turn a custom .exe or .msi into an .intunewin file with IntuneWinAppUtil, then deploy it as a Win32 app in Intune with install, uninstall and detection rules.
Enable Windows LAPS in Microsoft Entra, create the Intune account protection policy, turn on the built-in Administrator and read the password in Intune.
Avoid duplicate users when linking an existing Office 365 tenant to AD Connect: scripts to match users, sync proxyAddresses and set ImmutableIDs.
Add company branding to the Azure AD sign-in experience of your tenant. Video continuation of the Hybrid Join and Intune setup series.
Entra (Azure AD) join fails with 8018000a, device already enrolled: a PowerShell script removes the stale enrollment, then you delete the old device.
Install Azure AD Connect on Server 2022, start with a test group, add Seamless SSO via GPO and group-based licensing, then extend the sync to all OUs.